Railway Forces Secret Rotation After Breach Targets AI Platforms
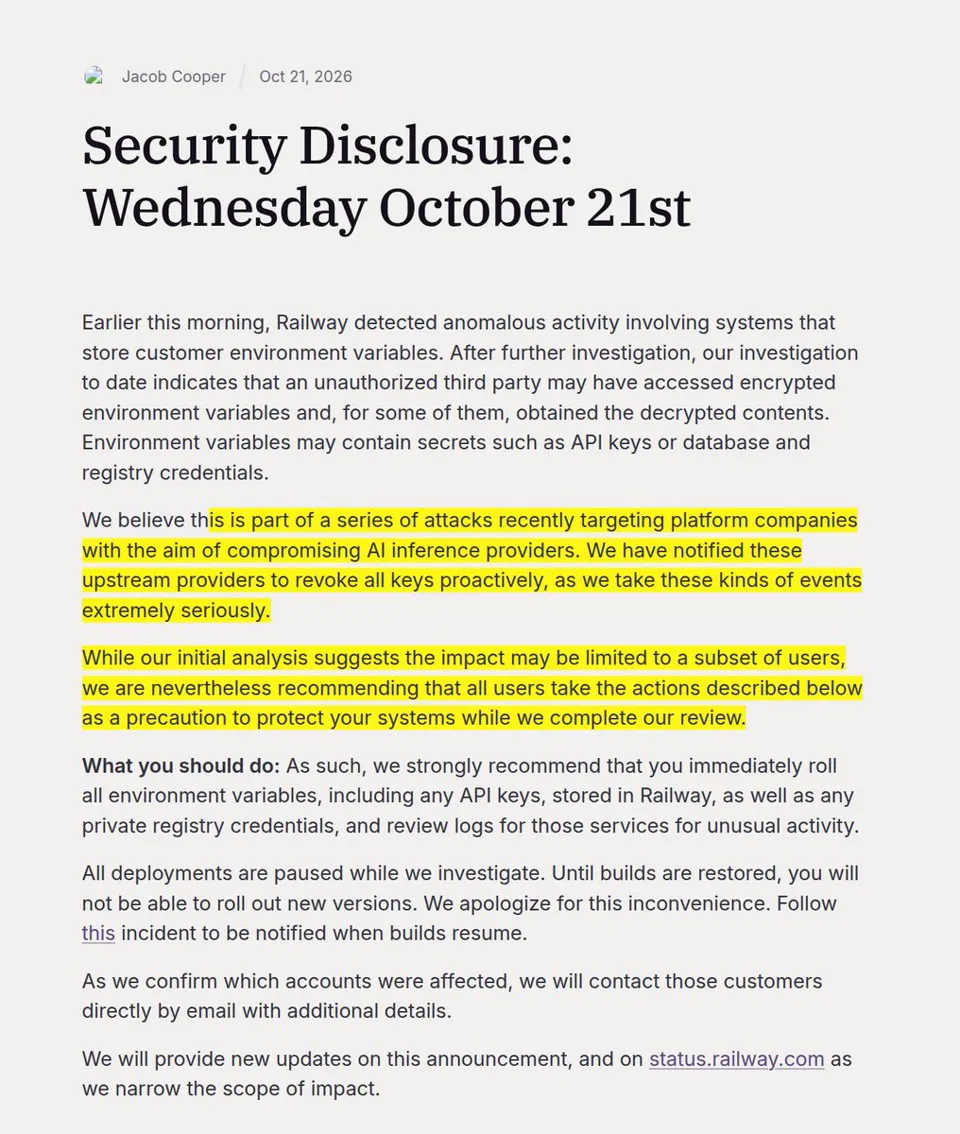
Developer platform Railway mandated secret rotation for all customers after an intruder decrypted stored credentials, including model API keys. The incident is linked to a series of attacks targeting AI inference providers to harvest frontier-model data for training rival models, following a similar breach reported by OpenCode.
Full Report
Rohan Paul (@rohanpaul_ai) · 2026-10-22 14
Developer platform Railway told every customer to rotate all secrets after an intruder decrypted some stored credentials.
Those environment variables hold database passwords, cloud keys and model API keys, letting anyone holding them sign in as the owner.
Railway said a subset of users may be affected, yet it froze all deployments and reset bucket keys and GitHub tokens itself.
It tied the intrusion to a string of attacks on platforms aimed at AI inference providers, and asked those providers to revoke keys.
Days earlier, OpenCode blamed a distillation attack for a breach possibly exposing OpenAI, Anthropic and Google keys saved by 1.4% of Console users.
Stolen keys let attackers harvest frontier-model answers for training rival models while victims pay the bills.